Recommended CMMC Program Changes | SecureITSM Response to the DoW CMMC RFI
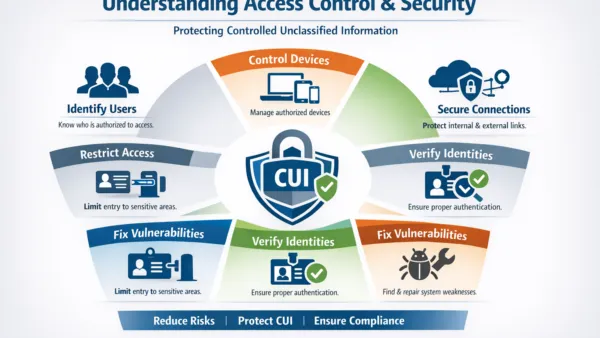
In this video, David Fraley, CTO of SecureITSM, shares practical recommendations for improving the Cybersecurity Maturity Model Certification (CMMC) program following the Department of War's Request for Information (RFI). The video discusses NIST SP 800-171 compliance, System Security Plans (SSPs), AI-assisted SPRS reviews, CMMC certification recommendations, assessment improvements, and technical considerations for future program enhancements. Watch to understand SecureITSM's perspective on making compliance more practical while maintaining strong cybersecurity standards.