SecureITSM provides complete managed IT for federal contractors and local governments with 10–100 systems—from everyday IT support and cybersecurity to Microsoft cloud, infrastructure, monitoring, and IT strategy.
Your technology should help your organization succeed—not slow it down. As a managed IT services provider, SecureITSM brings together managed IT support services, cloud services, cybersecurity, networks, devices, and IT management into one integrated solution. We keep your technology secure, reliable, and running smoothly so your people can stay productive and your organization can focus on what it does best.
SecureITSM provides comprehensive managed IT support for federal contractors that need reliable technology, responsive service, and strong cybersecurity. We manage users, devices, Microsoft cloud services, networks, infrastructure, monitoring, and security as one integrated environment—giving your organization the IT capabilities and expertise it needs without having to build and manage everything in-house.
Local governments need dependable technology, strong cybersecurity, and responsive support while operating within limited budgets and resources. SecureITSM manages users, devices, Microsoft cloud services, networks, infrastructure, monitoring, and security as one integrated environment—helping reduce risk, improve reliability, and keep critical government services running.
Tailored for organizations supporting federal agencies such as DHS, Commerce, or DOE that must comply with NIST 800-171 but are not subject to CMMC. SecureITSM combines managed IT security services, policy-driven governance, system hardening, documentation, evidence automation, and audit-ready reporting within your existing Microsoft cloud or hybrid infrastructure.
Purpose-built for organizations managing Controlled Unclassified Information (CUI) within DoD programs. SecureITSM provides managed IT security services across GCC or GCC High environments, Zero Trust architecture, Entra ID conditional access, Intune compliance, Defender XDR, and continuous compliance support aligned with NIST 800-171 and CMMC Level 2 requirements. We also support automated documentation, control tracking, and readiness for C3PAO assessment.
Our integrated approach unites managed IT support, cybersecurity, Microsoft cloud services, infrastructure, and compliance automation—keeping your operations secure, efficient, and always operational.

Provide responsive managed IT support for users, accounts, applications, workstations, onboarding/offboarding, and day-to-day productivity.

Manage the full device lifecycle, including MDM, RMM, software, configuration, inventory, compliance, patching, and endpoint security.

Protect the environment with managed security services that detect, investigate, respond to, and remediate cybersecurity threats.

Manage firewalls, switches, wireless, VPN, WAN/Internet connectivity, configuration, performance, and network security across the environment.

Design, deploy, migrate, configure, and modernize Microsoft cloud and IT infrastructure to establish a secure, fully managed environment.

Manage Microsoft 365, Azure and cloud services, on-premise servers, virtualization, storage, platforms, and applications within one integrated environment.

Protect critical data and services with managed backup, disaster recovery, and business continuity to maintain availability and restore operations quickly

Continuously monitor availability, health, performance, security, capacity, configuration, and operational conditions across your managed IT environment.

Manage ITSM, assets, vendors, licensing, reporting, planning, governance, budgeting, roadmaps, and vCIO/CISO functions to support long-term IT strategy.
We Achieved 110, Now It’s Your Turn
SecureITSM has completed a CMMC Level 2 audit with a perfect 110 score, proving our security controls, documentation process, and evidence readiness can stand up to real assessment scrutiny. As CMMC requirements move into DoD contract enforcement, we help contractors prepare with audit-ready managed IT, CUI protection, and NIST 800-171-aligned compliance operations.

We Built SecureITSM Because We Lived the CMMC Struggle
Claudia and David Fraley have run a successful DoD contracting business since 2008. They primarily provide cybersecurity and IT operational support to the U.S. Army. In 2016, when the DoD published DFARS 252.204-7012, which required DoD contractors to implement NIST 800-171, they knew it would cause problems for many DoD contractors. But as cybersecurity and managed IT experts, they successfully implemented NIST 800-171 within their operations.
When the DoD later released DFARS 252.204-7021, introducing CMMC, the Fraleys recognized that would create even bigger challenges for small vendors.
Therefore, in 2019, the Fraleys started SecureITSM as a CMMC Managed IT Service Provider (CMMC MSP). They knew small businesses would require expert help to achieve an audited level of compliance. Today, CMMC audits include more than 1,000 pages of documentation, dozens or even hundreds of evidentiary artifacts, and a level of expertise that few small businesses possess.
Today, Claudia runs Paragone Solutions, Inc., and David leads SecureITSM (a division of Paragone). Together, they help DoD contractors achieve continuous compliance through the Automated Documentation Manager App, Zero Trust architectures, and 24×7 managed cybersecurity operations, all built from real, hands-on experience in the field. SecureITSM is a CMMC MSP.

Manage firewalls, switches, wireless, VPN, WAN/Internet, connectivity, configuration, and performance.
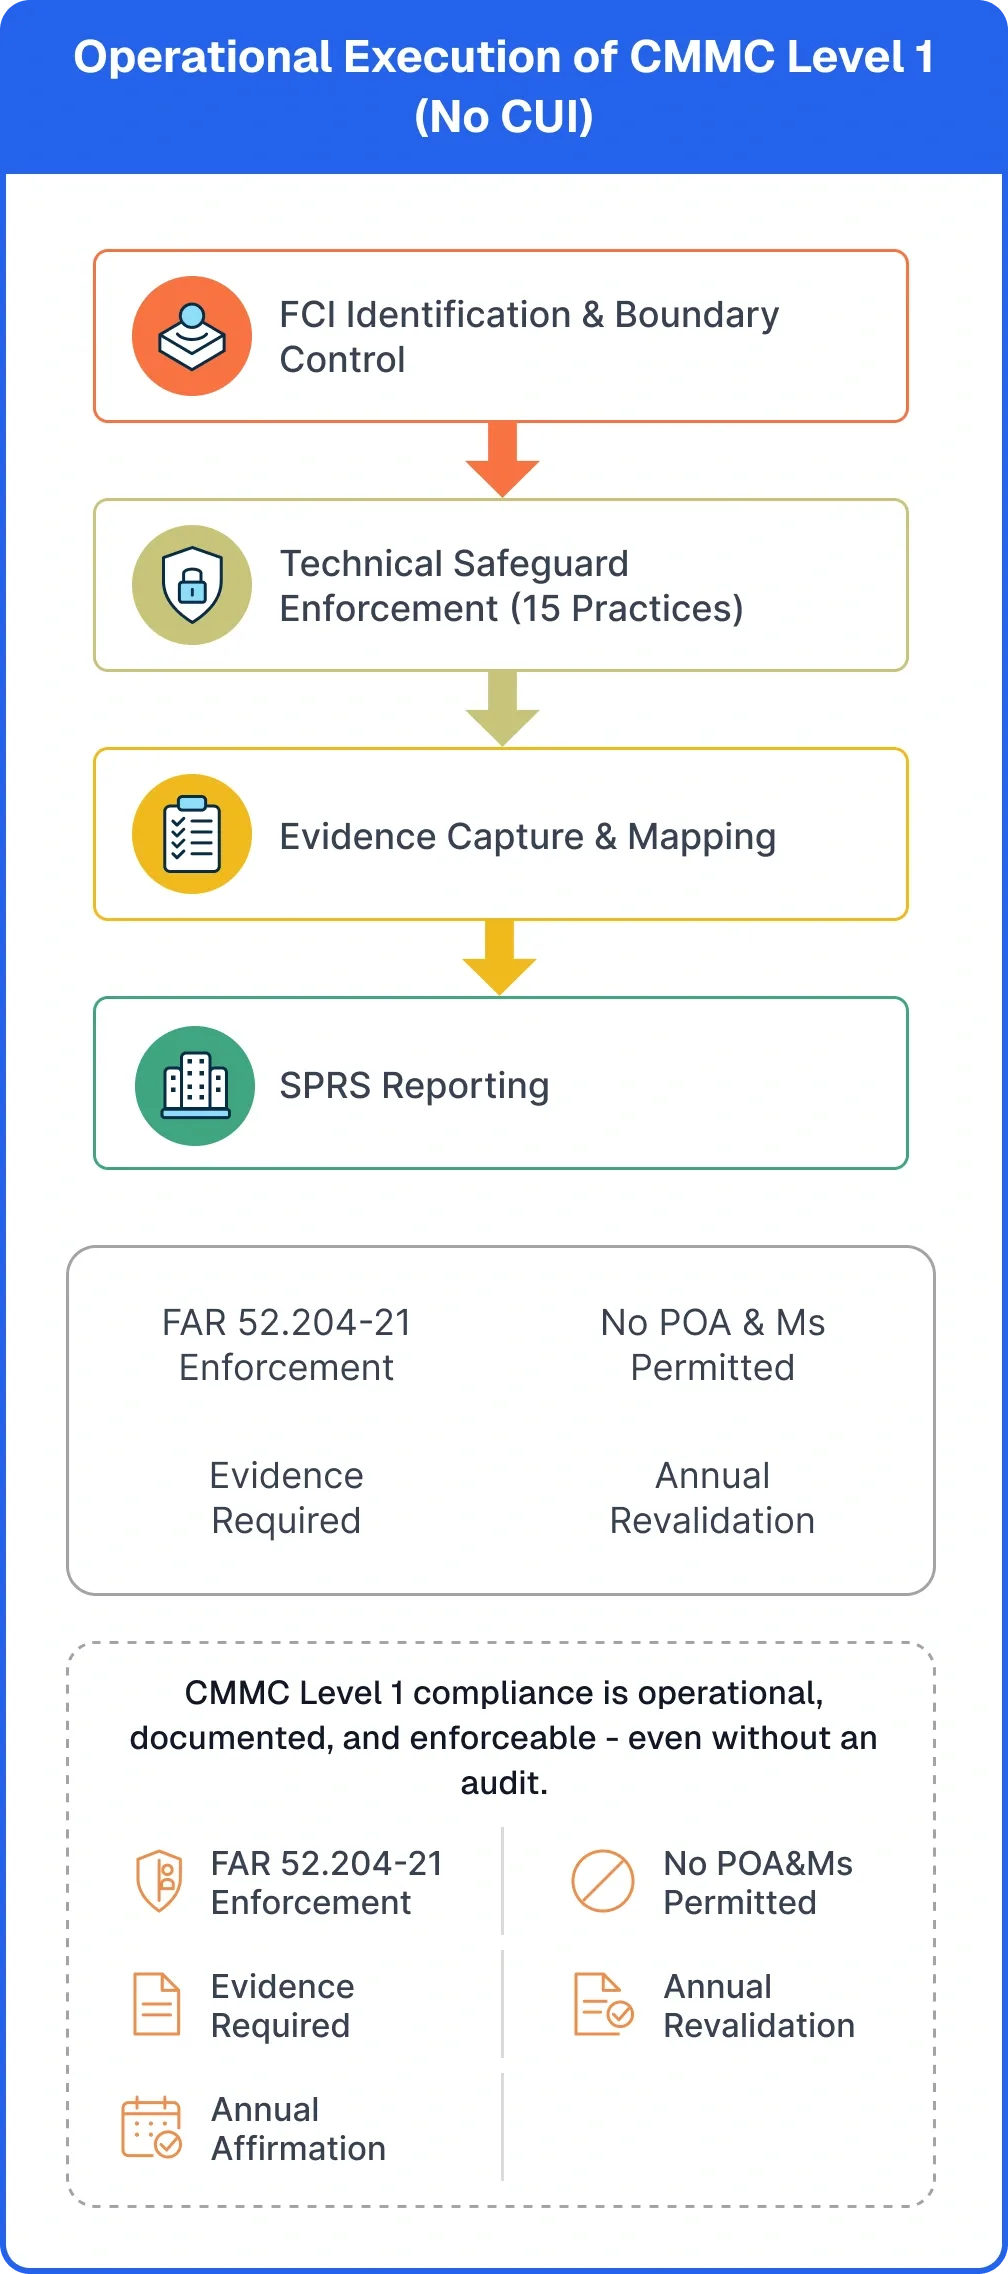
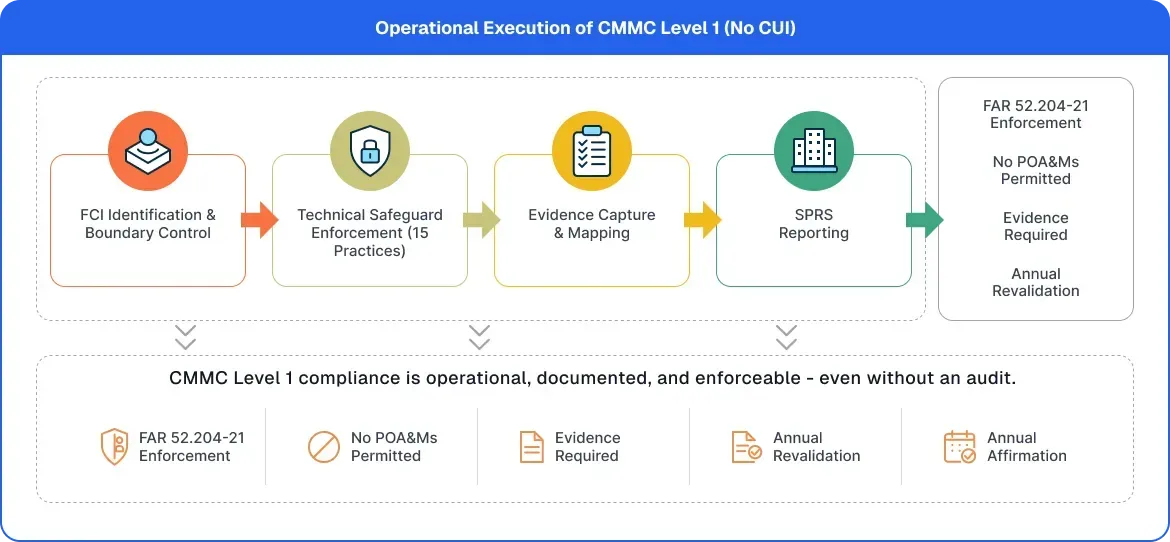
We define and validate where Federal Contract Information exists across email, file storage, collaboration tools, and systems establishing a defensible compliance boundary aligned to FAR 52.204-21.
Required policies and procedures are created and aligned directly to implemented safeguards, ensuring documentation reflects reality,not aspirational controls.
We confirm that all 15 Level 1 safeguards are fully implemented and operating, eliminating gaps that lead to false or unsupported affirmations .
Our team guides control scoring and interpretation to prevent overstatement, misclassification, or misalignment with assessment objectives.
We ensure your SPRS entry is complete, accurate, and evidence-supported reducing contractual and regulatory risk.
Senior official affirmations are backed by documented controls and repeatable processes, supporting long-term compliance sustainability.