SecureITSM delivers proactive IT support, infrastructure management, Microsoft cloud administration, and integrated cybersecurity for federal contractors and local governments—keeping your technology reliable, secure, and your team productive.
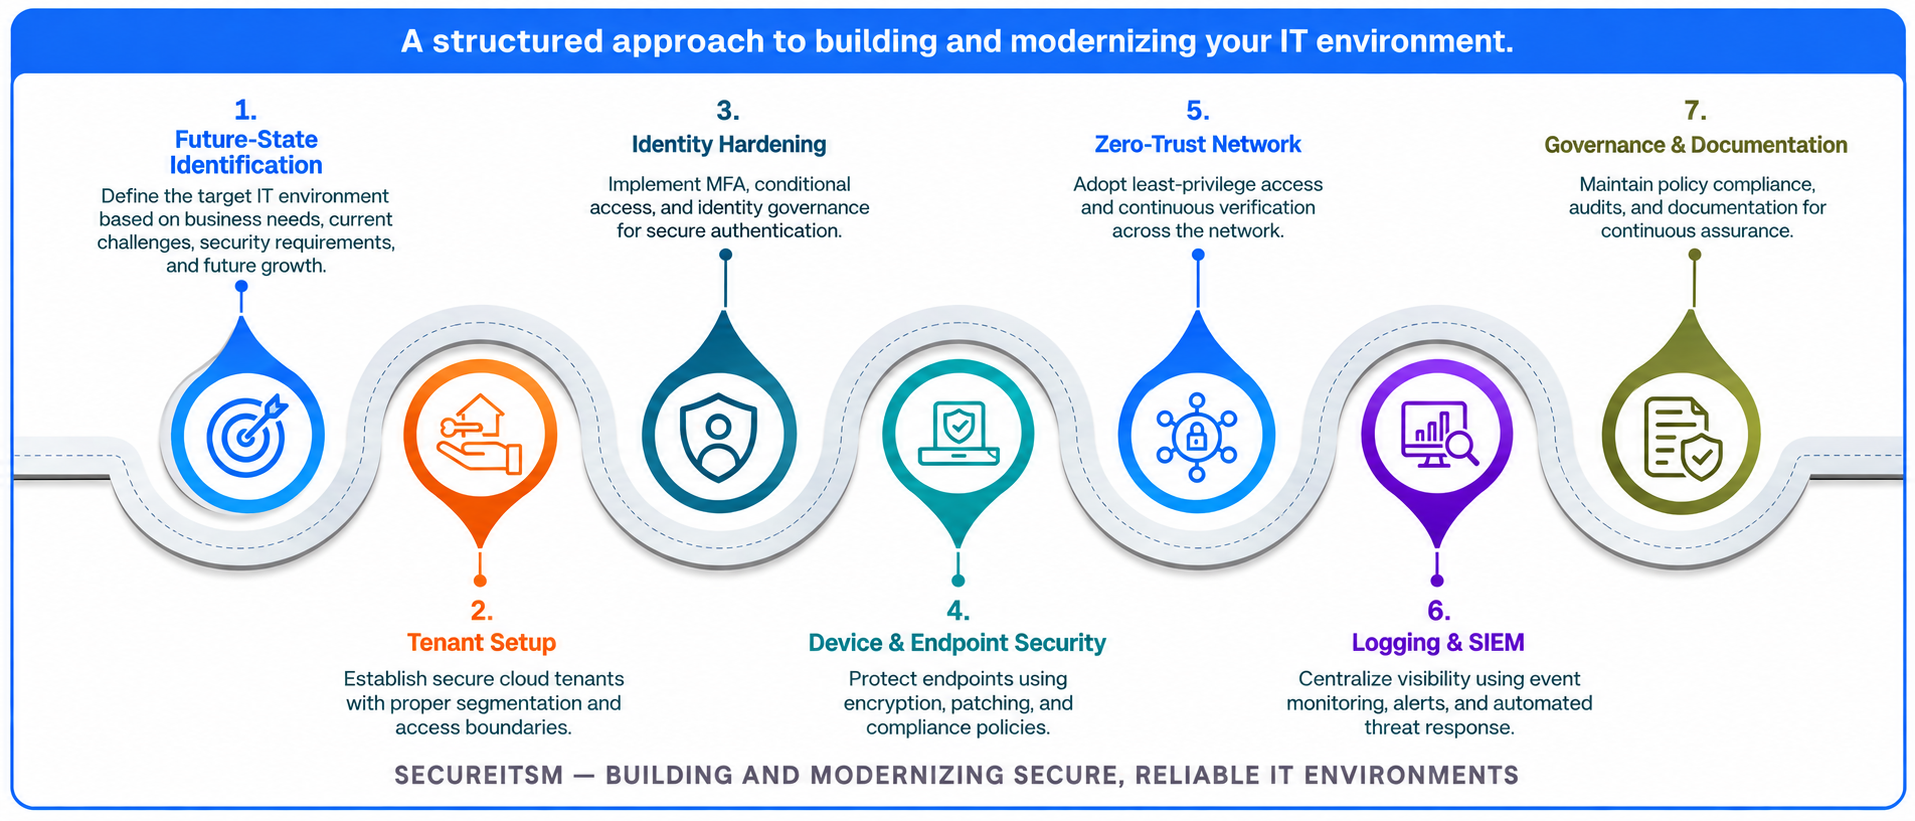
Whether building a new IT environment or modernizing an existing one, SecureITSM designs and implements the technology foundation your business needs. Our managed IT team deploys, migrates, configures, and secures your systems to create a reliable, manageable environment that supports daily operations and future growth.


SecureITSM provides responsive managed IT support through a structured escalation framework for defense contractors. From MFA and Microsoft 365 troubleshooting to endpoint, infrastructure, and security incidents, our specialists coordinate timely resolution to keep your IT operations secure and reliable.
Handles everyday IT support requests, password resets, MFA troubleshooting, Microsoft 365 access issues, and secure identity verification. Support tickets are logged and tracked to maintain accountability and ensure timely resolution.
Addresses system performance, patch deployment, Microsoft 365 and Azure application issues, and infrastructure configuration. Engineers troubleshoot complex technical problems and maintain secure, reliable IT operations.
Engages SecureITSM’s senior technical experts and third-party vendors to resolve complex issues involving applications, cloud platforms, and infrastructure. All escalations are documented and tracked through resolution.
Potential cybersecurity threats are escalated to the appropriate security specialists for investigation and response. Integrated security monitoring helps coordinate technical remediation, incident documentation, and communication when security issues affect IT operations.


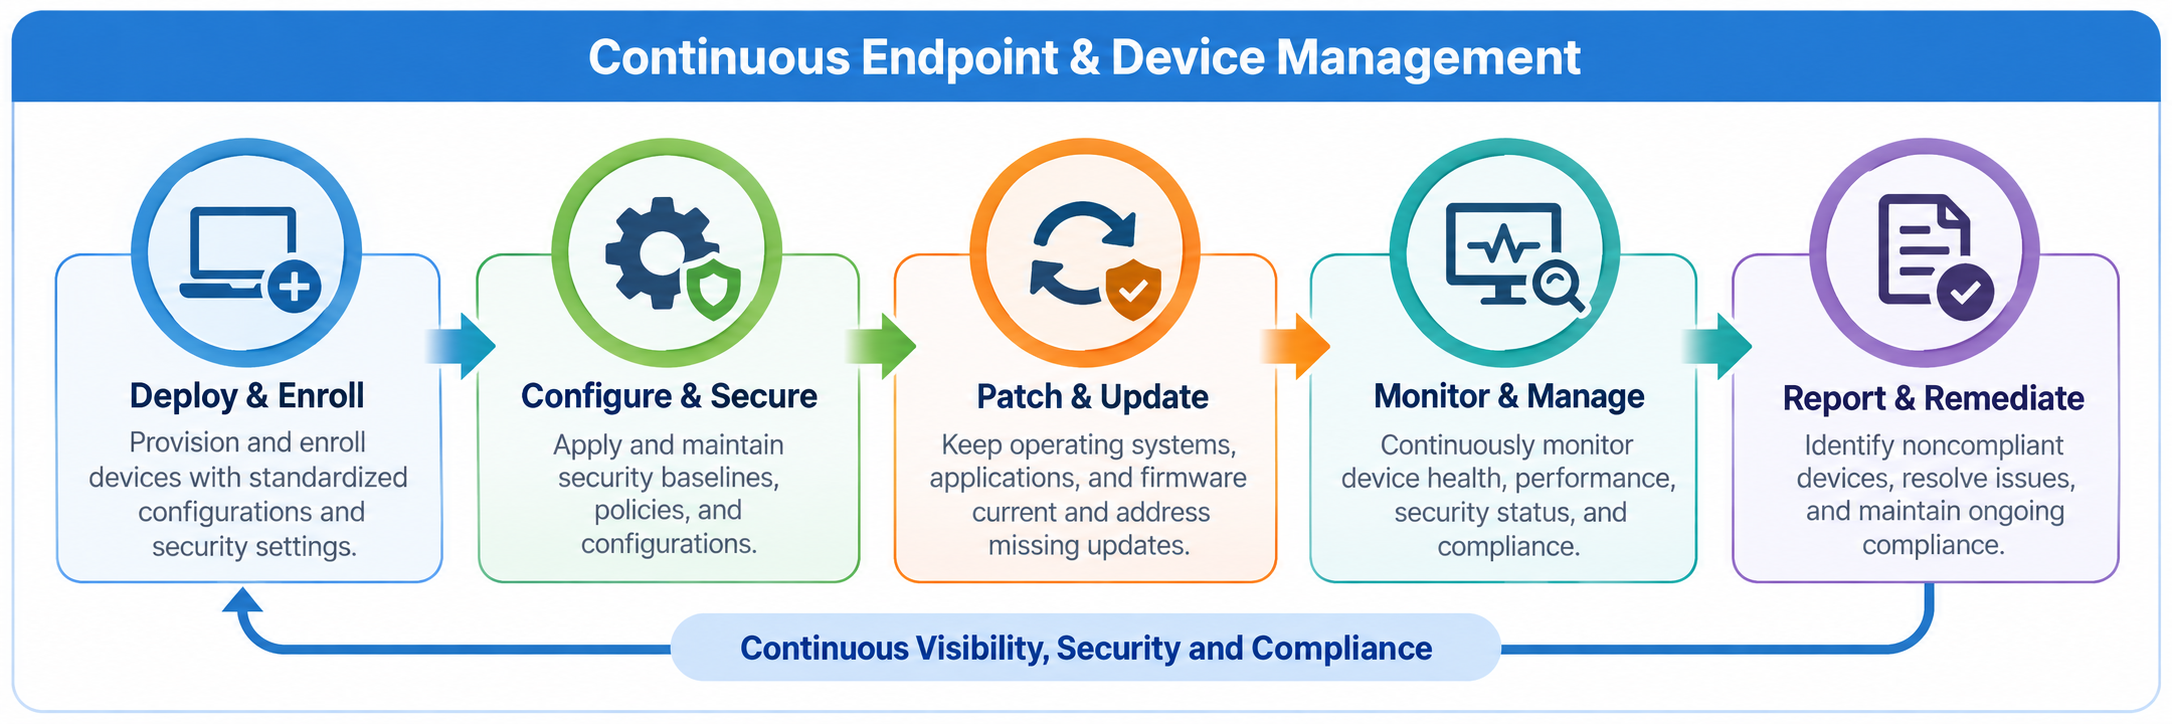
Manage the complete device lifecycle with Microsoft Intune, MDM, remote monitoring and management (RMM), software deployment, configuration, inventory, security, and patch management.
Maintain an accurate inventory of workstations, laptops, mobile devices, and other managed endpoints. Track ownership, status, configuration, warranty, and lifecycle from deployment through replacement and secure retirement.
Establish and maintain standardized device configurations and security settings using Microsoft Intune and other management tools. These baselines help ensure devices remain consistently configured and reduce security risks caused by configuration drift.
Keep operating systems, applications, firmware, and security components current through centralized patching and update management. Monitor deployment status, identify failed or missing updates, and address issues to maintain system security and reliability.
Use Remote Monitoring and Management (RMM) tools to continuously monitor device health, availability, performance, and security status. Identify issues early and maintain the visibility needed for proactive IT support and timely remediation.
Control the applications installed across managed devices, including deployment, updates, licensing, and removal. Standardize approved software while identifying and managing unauthorized or unnecessary applications.
Continuously evaluate devices against established configuration, security, patching, encryption, and organizational requirements. Identify noncompliant devices and remediate deficiencies to reduce operational and security risks.
Centralized Microsoft Sentinel monitoring with custom correlation rules, EDR integration, and UEBA analytics to detect anomalies, lateral movement, and identity threats in real time.
Predefined Microsoft Defender and Sentinel playbooks help isolate compromised assets, trigger forensic data collection, and coordinate automated remediation during security incidents.
Continuous threat hunting using KQL queries and integrated threat intelligence feeds helps identify hidden risks, investigate suspicious activity, and detect emerging attack patterns.
Centralized security dashboards provide visibility into threats, vulnerabilities, and remediation activities. Ongoing reporting helps track security posture, document incidents, and support NIST 800-171 compliance requirements.
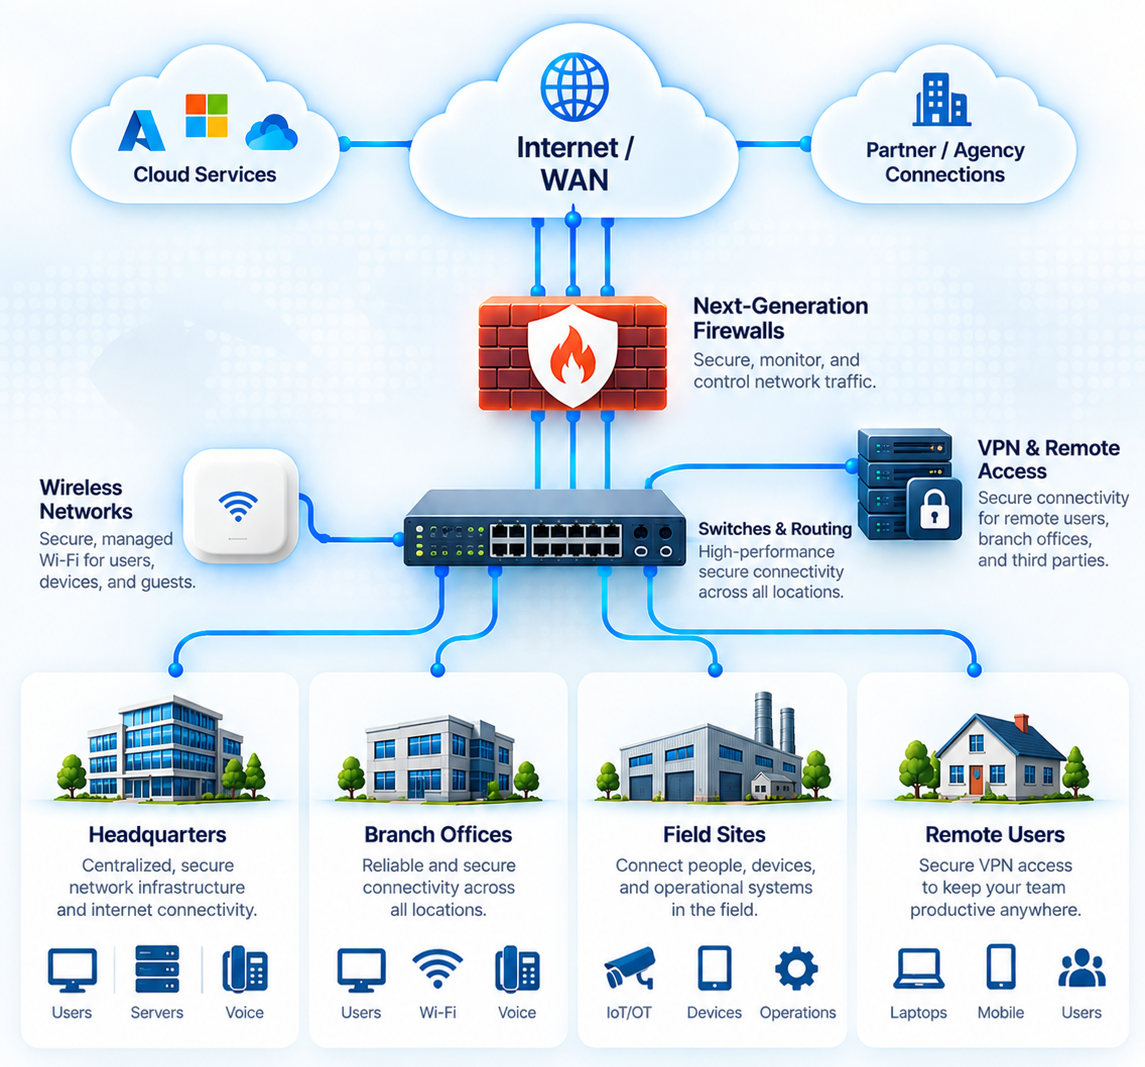
SecureITSM manages firewalls, switches, wireless networks, VPNs, WAN/Internet connectivity, and network configurations while monitoring performance, security, and availability to keep your IT operations connected and reliable.
24x7 Security Backed by DoD-Grade Standards
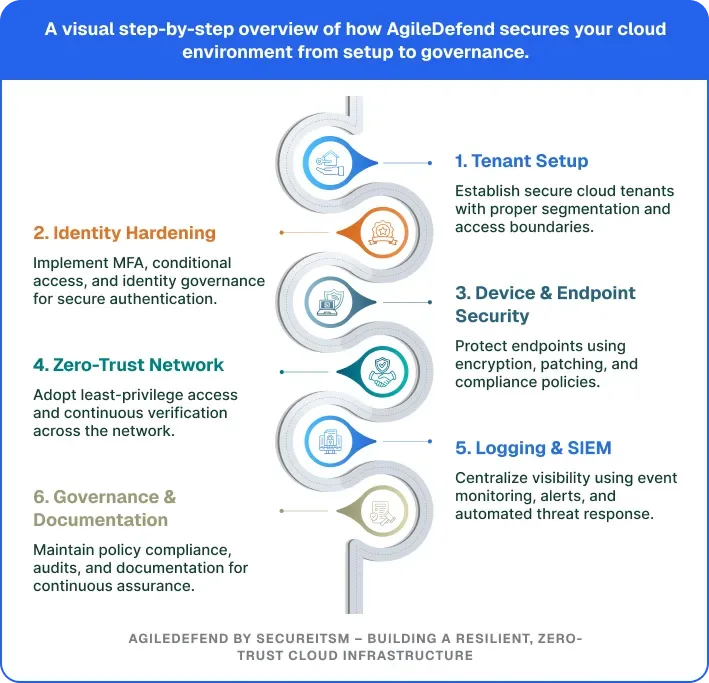
SecureITSM manages and secures Microsoft 365, Azure, and government cloud environments, including GCC and GCC High. Our team handles tenant configuration, identity and access management, Exchange, SharePoint, Teams, security baselines, and backup policies to keep cloud services secure, reliable, and aligned with operational and NIST 800-171 requirements.
We register domains, validate DNS records, and configure secure defaults for Microsoft GCC or GCC High tenants—supporting proper domain verification, licensing, and regional data residency requirements.
Access and administrative rights are assigned through Entra ID security groups, enabling least-privilege enforcement and data segregation between corporate and CUI environments.
Azure and Microsoft 365 services are deployed with CIS and DoD-aligned baselines, delivering automated logging, encryption enforcement, and telemetry integration for audit readiness.
Microsoft 365 data across Exchange, OneDrive, SharePoint, and Teams is protected through configured backup and retention policies, supporting data recovery, business continuity, and applicable government requirements.
SecureITSM protects your critical data, systems, and services while maintaining the ability to recover from disruptions. Our approach combines reliable backups, recovery planning, system resilience, and business continuity strategies to minimize downtime and keep your operations running.
We protect critical business data across cloud services, servers, endpoints, and applications using automated backups, secure storage, retention policies, and monitoring to ensure backups complete successfully.
We develop recovery strategies for critical systems and services, establishing recovery priorities and procedures to restore operations following hardware failures, cyber incidents, outages, or other disruptions.
We identify critical business functions and technology dependencies and develop continuity strategies that help your organization maintain essential operations when normal systems or facilities are unavailable.
We regularly validate backups and recovery procedures to confirm that protected data and systems can be restored when needed. Recovery documentation and testing help ensure your organization is prepared before an actual disruption occurs.
SecureITSM continuously monitors the availability, health, performance, security, capacity, and configuration of your IT environment. Centralized monitoring and automated alerts help identify issues early, support timely remediation, and keep systems secure, reliable, and performing as expected.
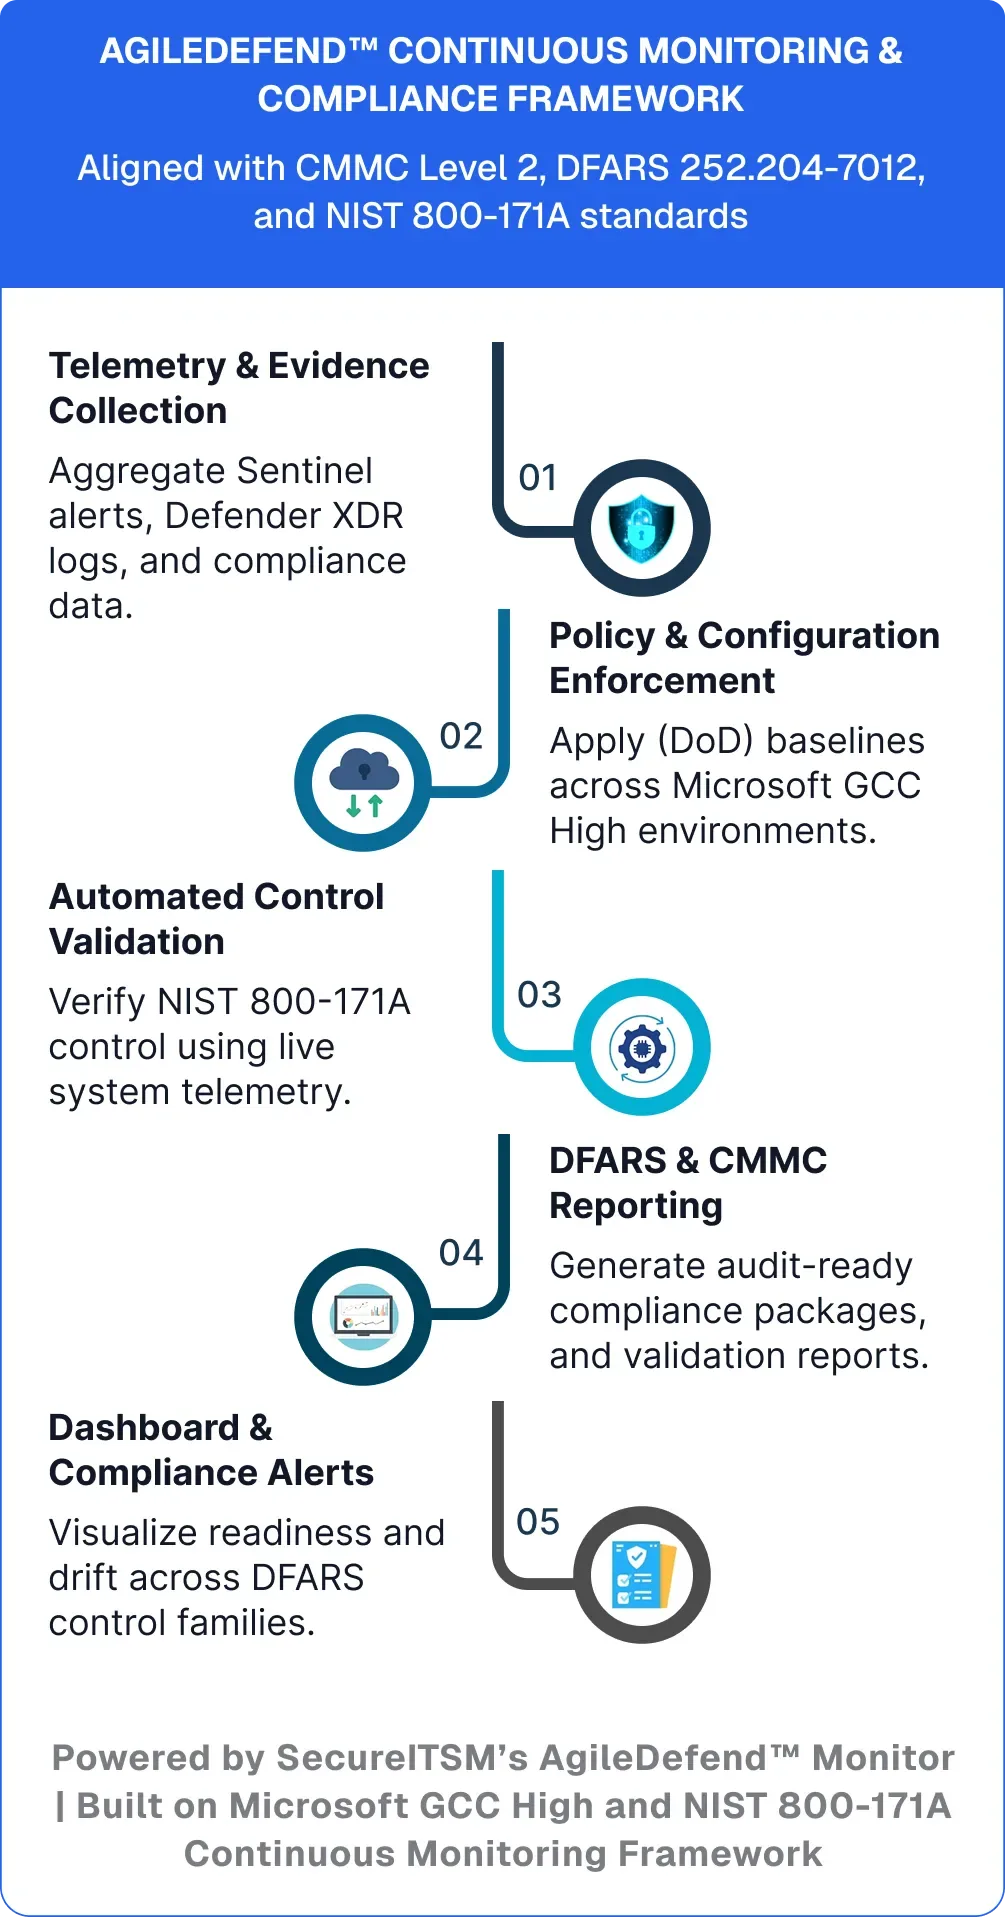
Detect configuration drift, system failures, security events, and performance issues through centralized monitoring and automated alerts.
Monitor identity, endpoint, and network configurations to identify changes, security gaps, and deviations from established IT standards.
Centralized dashboards provide visibility into system health, security alerts, configuration changes, and remediation activities across your IT environment.
Continuously monitor security configurations and system activity to identify vulnerabilities, suspicious changes, and potential operational risks.
Maintain visibility into secure environments and data protection controls, helping safeguard sensitive information across Microsoft government cloud services.
Review system configurations against established security baselines, identify control gaps, and track remediation activities to support ongoing security and NIST 800-171 requirements.
SecureITSM integrates IT lifecycle planning with cybersecurity, governance, and operational resilience. Our team aligns technology, assets, vendors, and IT policies with your business objectives while supporting NIST 800-171 requirements and long-term operational priorities.
We manage IT service delivery, processes, policies, documentation, reporting, and governance to provide consistent and accountable technology operations.
We manage technology assets, software licensing, subscriptions, renewals, and third-party vendors to improve visibility, control costs, and simplify administration.
We help develop IT budgets, forecast technology needs, prioritize investments, and plan hardware, software, cloud, and infrastructure expenditures.
We provide strategic technology and security leadership through IT roadmaps, executive reporting, risk planning, and vCIO/vCISO guidance aligned with your business priorities.
Federal and defense contractors trust SecureITSM to manage complex IT environments, strengthen cybersecurity, and support reliable day-to-day operations.

Raj R.CEO, , Foreign Military Sales Contractor
SecureITSM not only migrated us to Microsoft GCC High flawlessly but also securely integrated Salesforce into our controlled environment—something we once thought was impossible under strict DLA data boundaries. SecureITSM keeps our Microsoft and Salesforce systems continuously compliant and monitored, giving us complete confidence in a unified, zero-trust environment.
From everyday IT support to complex infrastructure and cybersecurity, SecureITSM helps federal contractors and local governments keep their technology secure, reliable, and running smoothly. Let's discuss what your organization needs.