CMMC Security Plan Documentation Tool

ITSM Control Manager — Automate CMMC Documentation & Simplify SSP Management

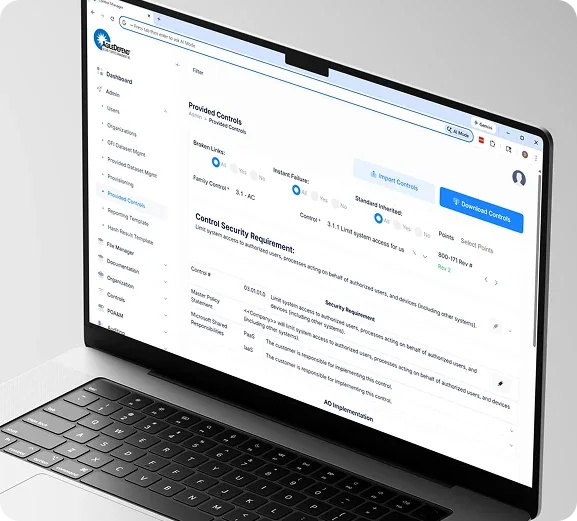
SecureITSM's proprietary Control Manager is a purpose-built CMMC documentation tool that helps federal contractors automate documentation, generate System Security Plans (SSPs), manage control inheritance, and prepare for C3PAO Level 2 assessments. It simplifies NIST 800-171 control documentation, annual security reviews, POA&M tracking, and risk analysis in one structured platform.
SecureITSM Security Dashboard
NIST 800-171 Documentation & Controls

Simplify CMMC Documentation & Security Control Management

To simplify CMMC documentation and shared control inheritance, SecureITSM developed Control Manager, a secure, cloud-based documentation tool purpose-built for federal contractors. It helps automate System Security Plan (SSP) generation, organize NIST 800-171 security controls, manage shared responsibilities, and track POA&Ms and annual security reviews—reducing documentation burdens and improving CMMC Level 2 assessment readiness.

Key Control Capabilities

  • Pre-Mapped Controls: NIST SP 800-171 and CMMC controls aligned to assessment objectives
  • Dynamic Evidence Management: Versioned, timestamped, and traceable artifacts
  • Integrated POA&M Tracking: Deficiencies managed alongside evidence
  • Instant Audit Reporting: SSPs, POA&Ms, and evidence summaries on demand
  • Continuous Monitoring Integration: Real-time security data linked to compliance records

When paired with SecureITSM™ managed security services, Control ensures continuous audit readiness, not last-minute preparation.
SecureITSM Security Dashboard
CMMC Documentation & Shared Control Inheritance

Control Manager — CMMC Documentation & SSP Automation

SecureITSM's Control Manager simplifies CMMC Level 2 documentation by organizing NIST 800-171 security controls, policies, responsibilities, and System Security Plans (SSPs) in one structured application. It helps federal contractors reduce repetitive documentation, clarify shared control inheritance, and maintain consistent records for ongoing assessment readiness.

Customer Specific Functionality

From the customer’s perspective, SecureITSM™’s Control Manager removes the complexity of CMMC compliance by eliminating redundant work, clarifying responsibility boundaries, and automating documentation requirements. The platform is designed so customers focus only on the NIST 800-171 security controls they are responsible for—while securely inheriting managed service provider (MSP) controls without having to recreate or defend them independently.

At the core of this value is structured control inheritance. MSP-implemented safeguards are formally documented, mapped, and made inheritable within the Shared Responsibility Matrix (SRM). Customers clearly see which controls are:

  • Fully inherited from SecureITSM™’s managed environment
  • Shared between customer and MSP
  • Fully customer-responsible

This eliminates duplication of effort, simplifies CMMC security control documentation, and prevents customers from addressing controls outside their authorization boundary.

Customer-focused capabilities include:

  • Automated SPRS score calculations aligned to NIST SP 800-171 scoring methodology
  • Dynamic Shared Responsibility Matrix defining security control ownership and inheritance
  • Custom policy and procedure documentation tailored to the customer environment
  • Auto-generated architectural diagrams reflecting the authorized boundary
  • Custom cybersecurity risk analysis, risk register, and executive reporting
  • Automated System Security Plan (SSP) generation aligned to NIST 800-171 assessment objectives

Dedicated CMMC Level 2 pre-assessment preparation pages guide customers through artifact readiness, evidence validation, and objective-level review before engaging a C3PAO.

The result is a structured, assessment-ready compliance posture that reduces internal documentation burden while increasing confidence at CMMC Level 2.

Shared Responsibility Matrix

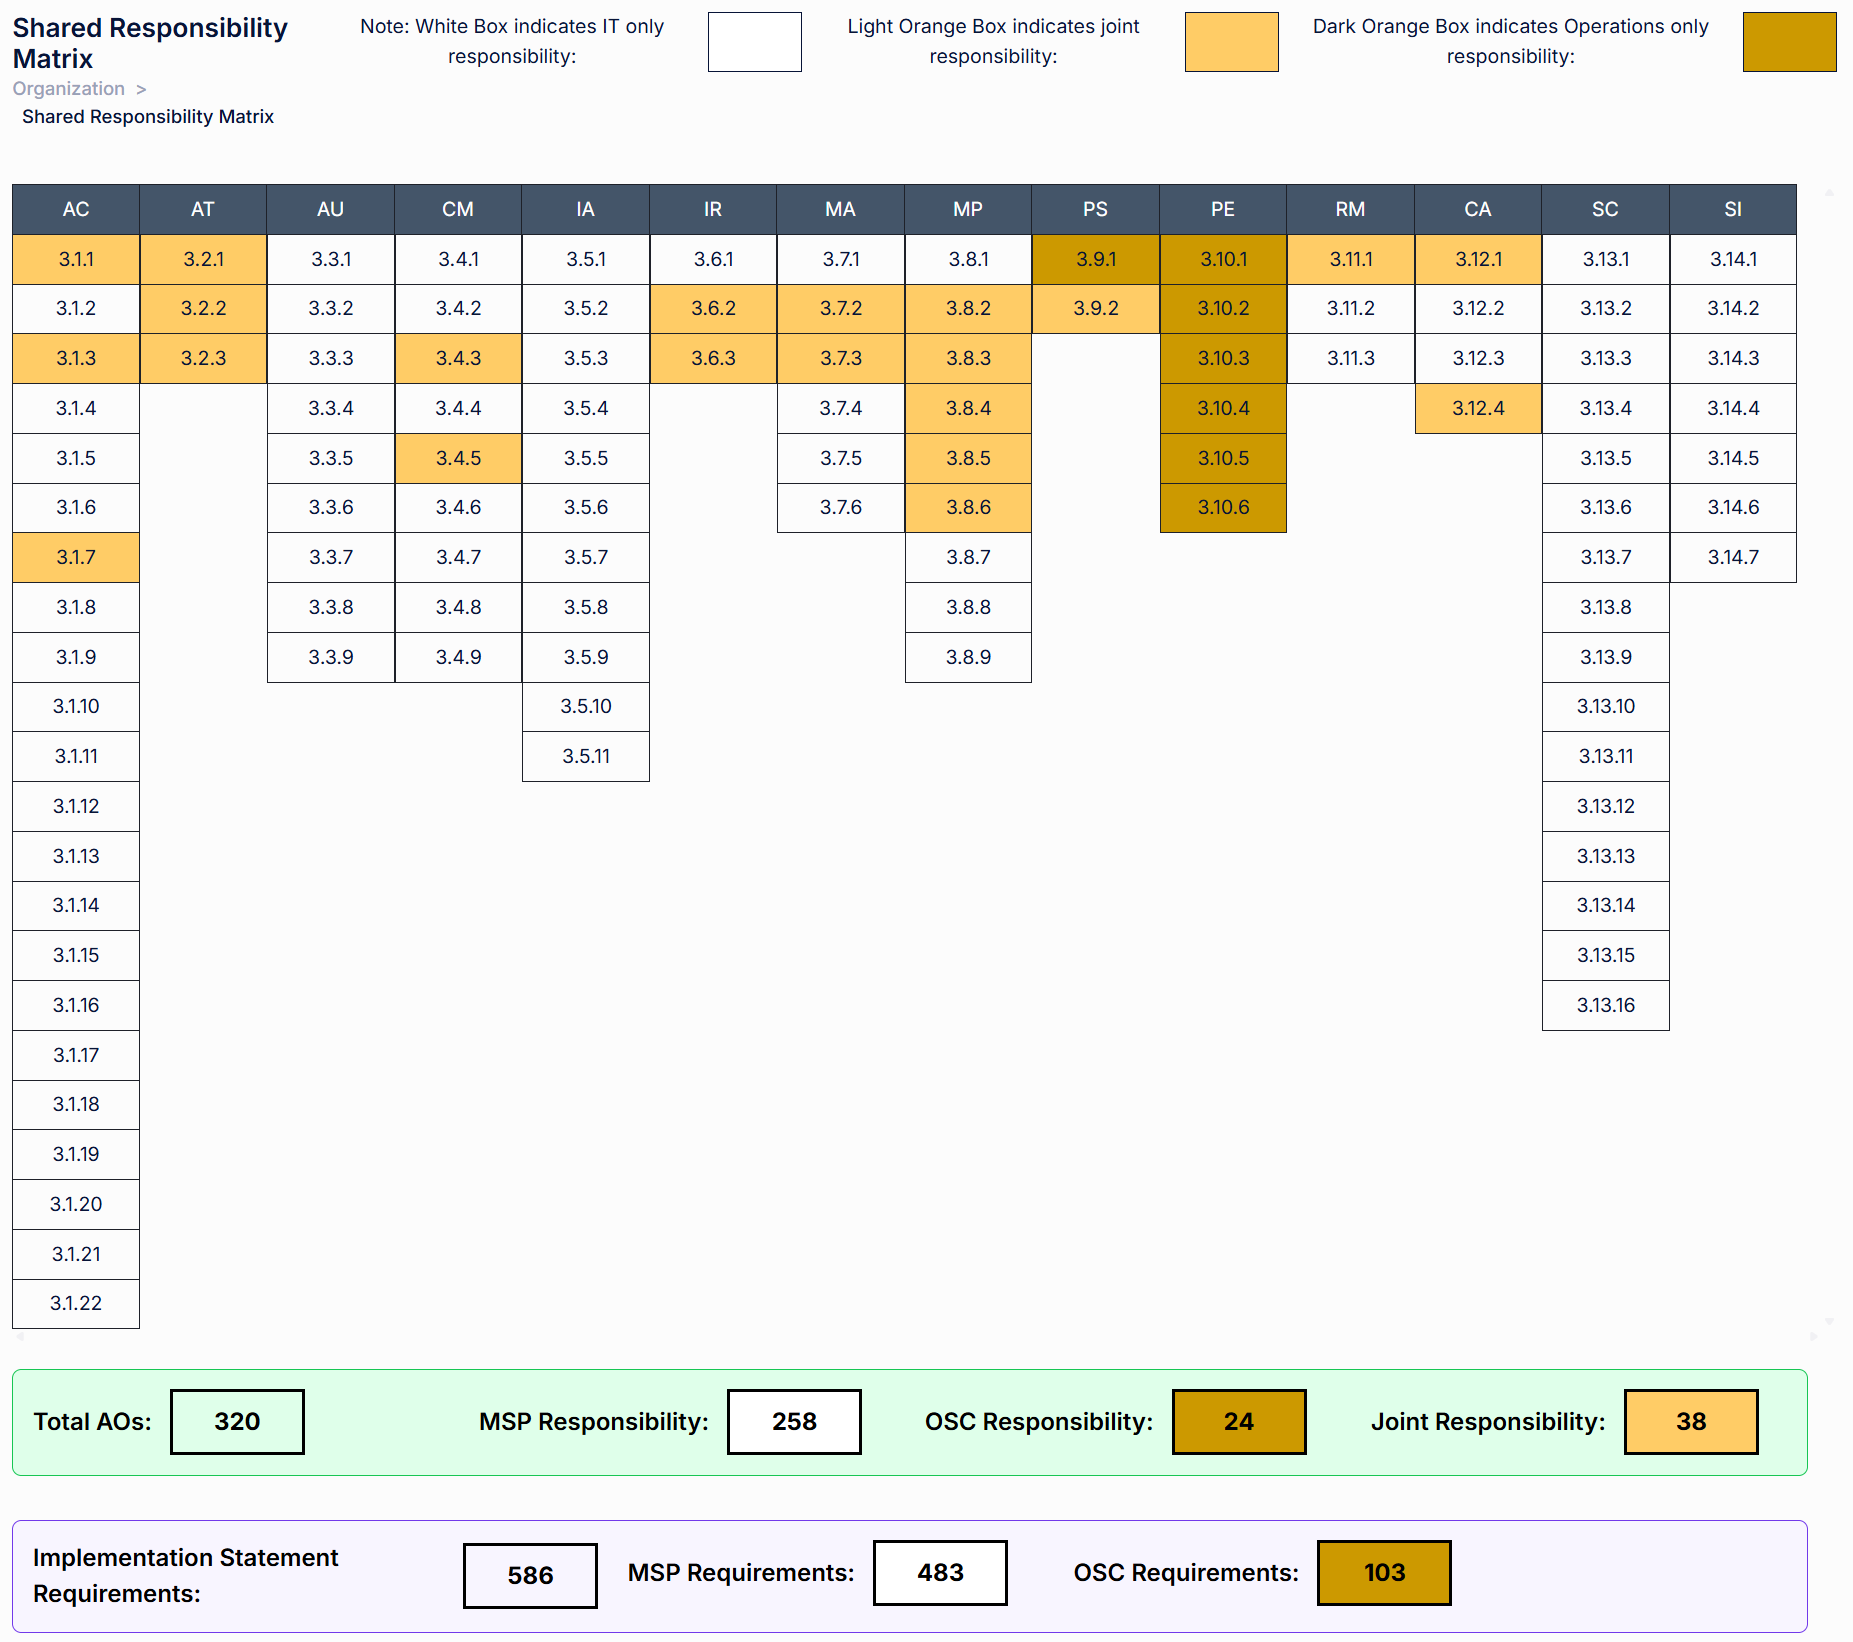
SecureITSM’s Shared Responsibility Matrix (SRM) is a core feature of our proprietary Control Manager CMMC Documentation Management Application — a purpose-built platform engineered to manage the full lifecycle of CMMC documentation within a secure GCC-hosted virtual environment.

Unlike generic GRC tools, Control Manager was designed specifically for CMMC. The embedded SRM provides precise, objective-level accountability mapping across all 320 CMMC Assessment Objectives and 586 implementation statements, clearly defining which responsibilities are fulfilled by the Managed Service Provider (MSP) and which remain with the organization.

Key insights from our SRM analysis:

  • 80.6% of the 320 CMMC Assessment Objectives are MSP-provided
  • 82.4% of the 586 implementation statements are MSP-provided

This data-driven clarity eliminates ambiguity during assessment preparation and audit execution. Organizations gain a defensible, documented view of:

  • Control ownership
  • Evidence responsibility
  • Implementation accountability
  • Continuous monitoring obligations

By quantifying responsibility at the assessment-objective level, Control Manager reduces audit risk, prevents duplicated effort, and ensures no requirement is unintentionally unassigned.

The result is measurable transparency between client and provider, streamlined C3PAO readiness, and a defensible compliance posture built on clearly documented shared accountability.

Control Manager doesn’t just store documentation — it operationalizes responsibility.
SecureITSM Security Dashboard
CMMC Findings & Outcome Handling

CMMC Post-Assessment & Findings Support

Completing a CMMC Level 2 assessment introduces a critical transition phase. SecureITSM supports assessment findings documentation, evidence clarification, and POA&M coordination without guaranteeing outcomes or bypassing formal assessment processes.

1

Findings Documentation Support.

CMMC assessment findings are organized, contextualized, and prepared for lifecycle transition without reinterpretation.

2

POA&M Coordination (Where Applicable).

Where remediation planning is required, SecureITSM supports structured POA&M development and tracking aligned to assessment results.

3

Certification Outcome Support.

We assist with evidence clarification and next-step planning without certification guarantees or assessor interference.

Designed for CMMC Level 2 Assessments

Why SecureITSM’s CMMC Assessment Support Model Is Different

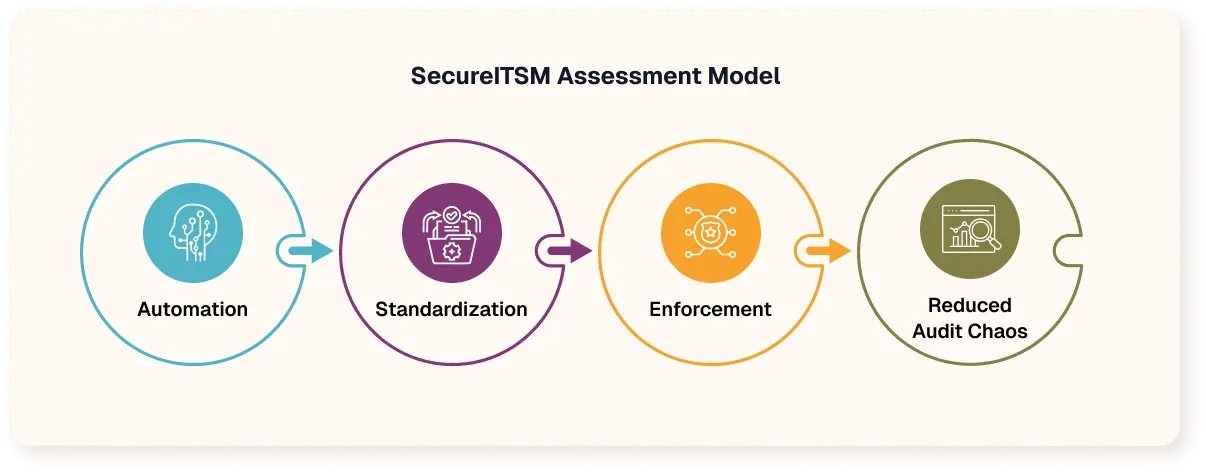
Key to our CMMC assessment support model is our proprietary Control Manager application, documentation automation, and hands-on guidance throughout the CMMC Level 2 assessment process. SecureITSM replaces ad-hoc consulting with standardized workflows, security control documentation, automation, and an enforcement-driven operating model.

SecureITSM Security Dashboard

C3PAO Specific Functionality

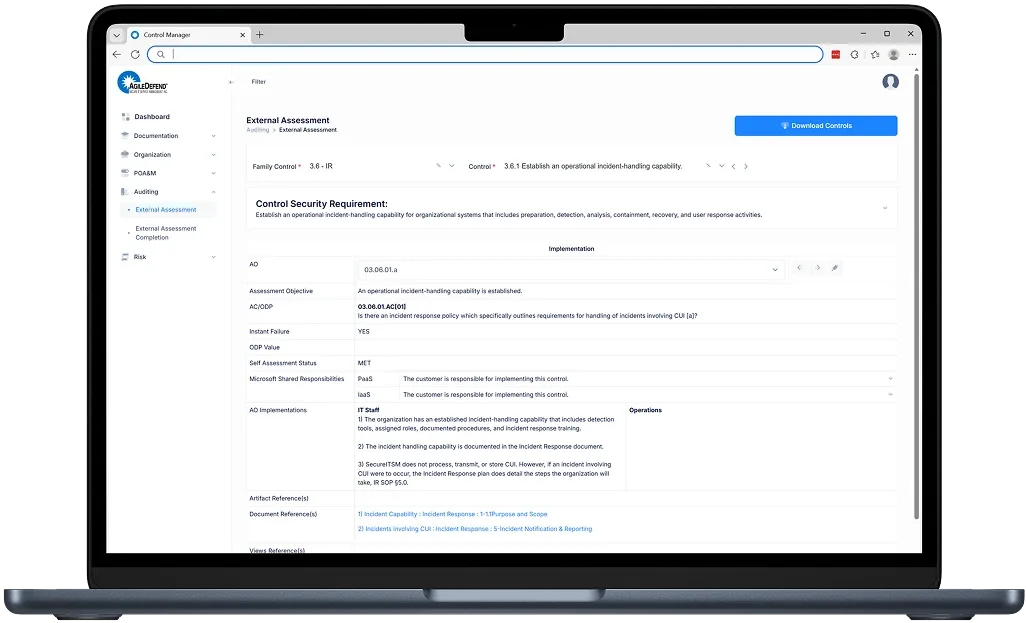
Control Manager reduces CMMC Level 2 assessment friction by organizing all required artifacts in direct alignment with NIST SP 800-171 and CMMC Level 2 assessment objectives. Each control is pre-mapped to its corresponding practice and objective, allowing organizations to maintain audit-ready narratives, artifacts, and implementation evidence throughout the system lifecycle rather than assembling them reactively during an audit window.
  • Centralized documentation repository mapped directly to assessment objectives
  • Shared Responsibility Matrix clarifying control ownership, inheritance, and boundary scoping
  • Integrated POA&M management aligned to DoD formatting and submission expectations
  • Pre-structured Auditor Page compiling required assessment artifacts in assessment-ready format

The Auditor Page serves as the authoritative assessment package, consolidating all materials required for submission to eMASS at the conclusion of a C3PAO assessment. This includes structured control narratives, implementation statements, artifact references, objective-level evidence mapping, POA&M entries, and associated assessment results.

At assessment completion, Control Manager automatically generates the required cryptographic hash record for submission, ensuring artifact integrity and compliance with DoD validation requirements.

By maintaining continuous CMMC assessment readiness, enabling structured control inheritance, and automating final submission outputs, Control Manager transforms CMMC from a disruptive, point-in-time audit event into a controlled, repeatable compliance process aligned with SecureITSM’s managed IT and cybersecurity lifecycle methodology.
SecureITSM Security Dashboard
Our Control Manager Application

Control Manager FAQs

What is SecureITSM Control Manager?
arrow

Control Manager is SecureITSM’s proprietary application that automates CMMC documentation, evidence management, and control traceability across your environment.

How does Control Manager support CMMC compliance?
arrow

How does Control Manager automate documentation?
arrow

What makes Control Manager different from other compliance tools?
arrow

How does Control Manager integrate with SecureITSM's Managed IT services?
arrow

Can Control Manager generate a complete SSP?
arrow

How does Control Manager handle assessment objectives (AOs)?
arrow

Does Control Manager track evidence for CMMC audits?
arrow

How does Control Manager reduce CMMC assessment risk?
arrow

Can Control Manager identify compliance gaps?
arrow

Does Control Manager support ongoing compliance?
arrow

How does Control Manager handle shared responsibility environments (e.g., cloud)?
arrow

Can Control Manager be used with Microsoft 365 GCC High?
arrow

Is Control Manager only for CMMC?
arrow

How does Control Manager help during a C3PAO assessment?
arrow

Does Control Manager replace manual spreadsheets and documents?
arrow

How quickly can Control Manager be implemented?
arrow

Who should use Control Manager?
arrow

What problem does Control Manager solve?
arrow

How does Control Manager improve audit outcomes?
arrow

How can I get access to SecureITSM Control Manager?
arrow

Prepare for Your CMMC Assessment With Confidence

Get Expert Support for Your CMMC Level 2 Assessment

SecureITSM provides structured CMMC Level 2 assessment support, including evidence coordination, assessor interaction, and post-assessment continuity. Our standards-driven approach helps federal contractors navigate CMMC assessments with consistent documentation, clear responsibilities, and no shortcuts or certification guarantees.
Professional IT team collaborating